Government issues urgent cybersecurity update to all state institutions
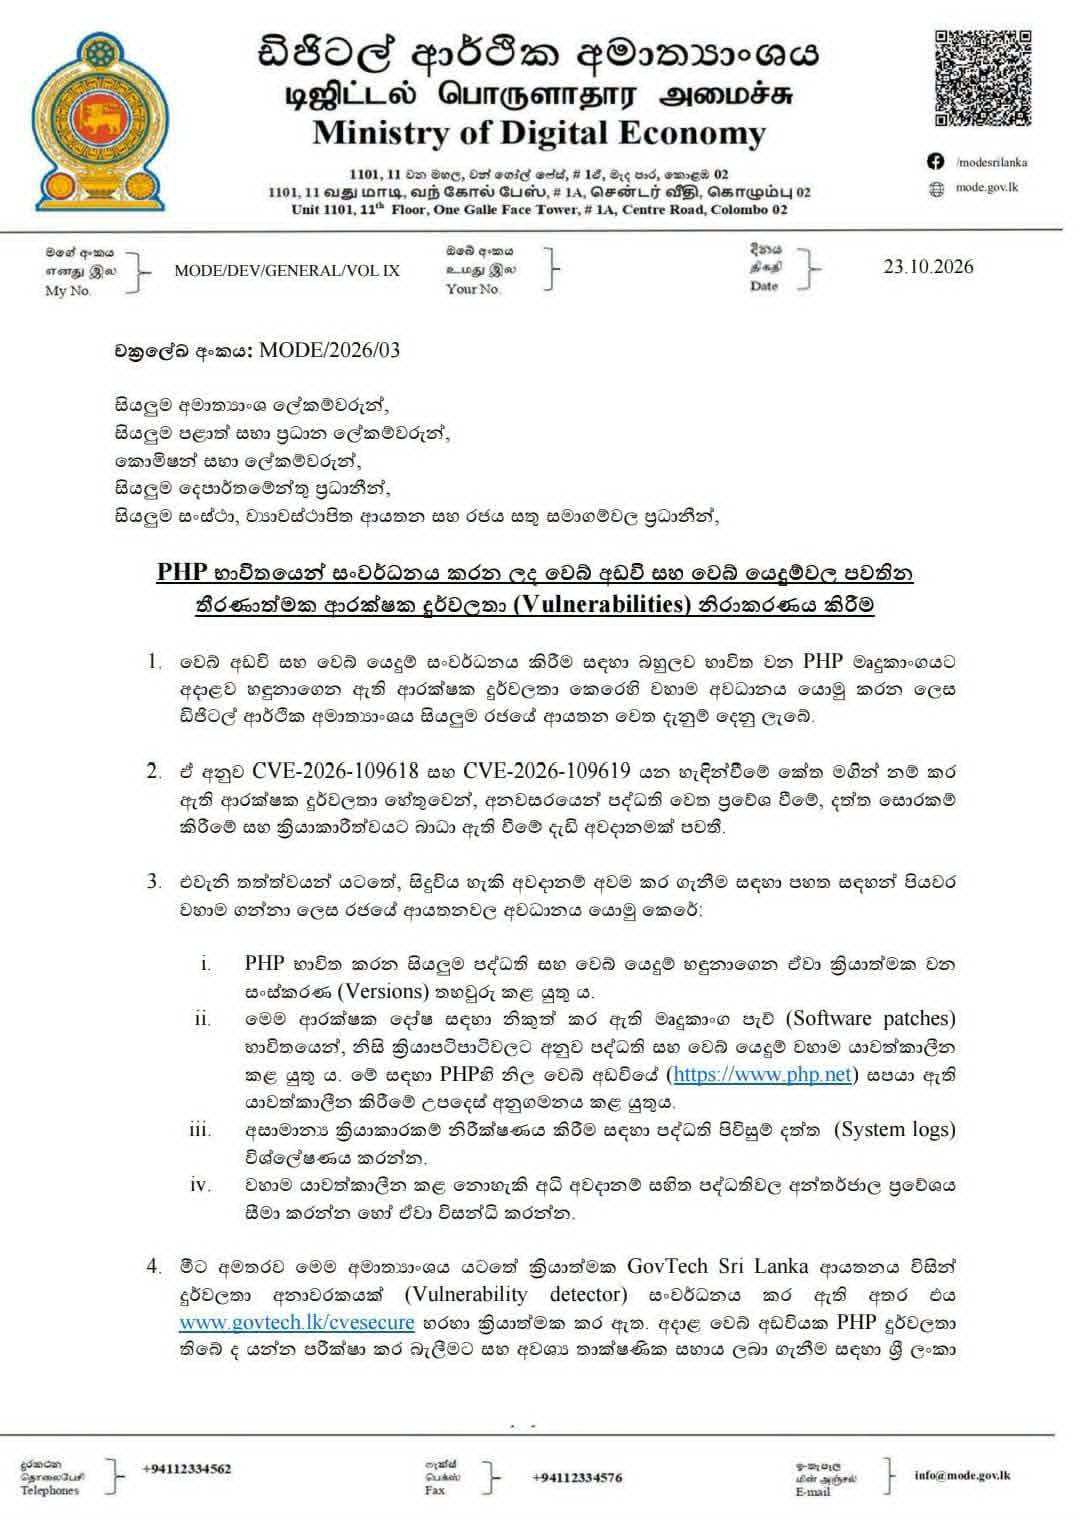
The Ministry of Digital Economy has directed all government institutions to take immediate action to address critical security vulnerabilities affecting websites and web applications developed using PHP software.
In a circular issued to ministry secretaries, department heads, provincial councils, commissions, statutory bodies and state-owned companies, the ministry warned that the vulnerabilities could expose government systems to unauthorized access, data theft and operational disruptions.
The circular, numbered MODE/2026/03 and signed by Ministry Secretary Waruna Sri Dhanapala, identifies two security vulnerabilities under the codes CVE-2026-109618 and CVE-2026-109619.
Government institutions have been instructed to identify all systems and web applications using PHP, verify their software versions and immediately install relevant security updates.
Officials have also been directed to examine system logs for suspicious activity and restrict internet access to high-risk systems that cannot be updated immediately.
The ministry said GovTech Sri Lanka has developed a vulnerability detection tool, accessible through www.govtech.lk/cvesecure, to help technical officers identify potential security weaknesses.
Institutions have also been advised to coordinate with Sri Lanka CERT for technical assistance.
The ministry stressed the need for immediate preventive measures to minimize potential cybersecurity risks across government digital infrastructure.
Local News
Litro to distribute 350,000 gas cylinders within three days
23 October 2026
Trending News
SIMs to be deactivated on unregistered new mobile devices from tomorrow
30 September 2020
CSE ASPI touch all-time high of 10,037.61
27 October 2021
Popular actress Sureni Senarath passes away
26 May 2021